
What are the Microsoft 365 security best practices every Brisbane small business should follow? Microsoft 365 holds your email, your files, your Teams conversations and your client data. One stolen password can open all of it.
The good news is that most of the protection you need comes from settings, not new software. This guide walks through 10 practical steps, from multi-factor authentication to backups. It also shows how to measure your progress with Secure Score and how these steps line up with the Essential Eight.
It is written for owners and office managers of Brisbane, Gold Coast and Sunshine Coast businesses who want a clear checklist rather than a vendor manual.
Key Takeaways Microsoft 365 Security Best Practices
- Identity is the main target. Microsoft research shows multi-factor authentication (MFA) can block more than 99.2% of account compromise attacks. It is the first of the Microsoft 365 security best practices to put in place.
- Your licence decides your toolkit. Business Premium includes Entra ID P1 (for Conditional Access), Intune, Defender for Business and Defender for Office 365 Plan 1. Business Standard does not.
- Keep administrator access small. Microsoft recommends fewer than five Global Administrators, plus two emergency access accounts.
- Email, apps and sharing need attention too. Phishing protection, third-party app consent and external sharing defaults are common weak points.
- Backup is not the same as retention. Recycle bins and retention settings do not replace a proper backup of your Microsoft 365 data.
- Review it monthly. Secure Score in the Microsoft Defender portal shows what to fix next.
Quick Answer For Microsoft 365 Security Best Practices
The most important Microsoft 365 security best practices are: enforce MFA for every user, block legacy authentication, use Conditional Access, protect administrator accounts, and switch on anti-phishing protection.
Additionally, restrict third-party app consent, manage devices with Intune and Defender, tighten SharePoint and OneDrive sharing, protect sensitive data with labels and data loss prevention, and back up your data separately.
Check your progress monthly using Secure Score. For most Brisbane SMBs, Microsoft 365 Business Premium provides the tools for nine of these ten steps. Backup needs a separate service.
Why Microsoft 365 Security Best Practices Matter for Brisbane SMBs
Microsoft secures the cloud service itself. How your tenant is configured is up to you, and that is where many small businesses are exposed. Three realities explain why the steps below matter.
One Login Unlocks Everything
A single Microsoft 365 account usually reaches email, OneDrive, SharePoint, Teams and any app that signs in with Microsoft. If an attacker takes over one account, they can read email, send convincing messages to your clients and download shared files. That is why the first steps in this guide focus on how people sign in, not on antivirus.
Attackers Go After People, Not Just Devices
Phishing is still the most common way into a Microsoft 365 account. Our guide to phishing attacks on SMBs in Australia covers the costs and warning signs. Newer attacks such as consent phishing go further. They trick a user into approving a malicious app, so no password is ever stolen.
Your Licence Decides Which Controls You Can Use
Not every control is available on every plan. Business Basic and Business Standard do not include Conditional Access, Intune device management or Defender for Business. Business Premium includes all three, along with Entra ID P1 and Defender for Office 365 Plan 1, and supports up to 300 users.
Australian resellers list Business Premium at around AU$32.90 per user per month, excluding GST, on an annual commitment (September 2026 pricing). Confirm current pricing before you budget. Our guide to Microsoft 365 Business Premium explains what each tier includes.
10 Microsoft 365 Security Best Practices to Put in Place
Work through these in order. The first four protect sign-in, which is where most attacks start.
1. Enforce Multi-Factor Authentication for Every User
Multi-factor authentication is the single most effective step on this list. To enable multi factor authentication, users must provide two or more verification methods to log in, which adds a second check beyond a password.
Microsoft’s own research shows MFA can block more than 99.2% of account compromise attacks. Microsoft has also been phasing in mandatory MFA for its admin portals, including the Microsoft 365 admin center. That requirement covers administrators only. Your staff mailboxes still need their own policy. Because over 80% of breaches involve human error, MFA helps limit the damage from stolen passwords and mistaken approvals.
Turn MFA on for every user, not just admins. If your plan does not include Conditional Access, Microsoft’s security defaults provide a basic MFA setup at no extra cost. Use the Microsoft Authenticator app with number matching rather than text message codes where possible. Number matching helps stop MFA fatigue attacks, where a user approves a prompt just to make it go away.
For administrators, move to phishing-resistant methods such as FIDO2 security keys or passkeys. Our guide to multi-factor authentication for SMBs explains why passwords alone are no longer enough.
2. Block Legacy Authentication
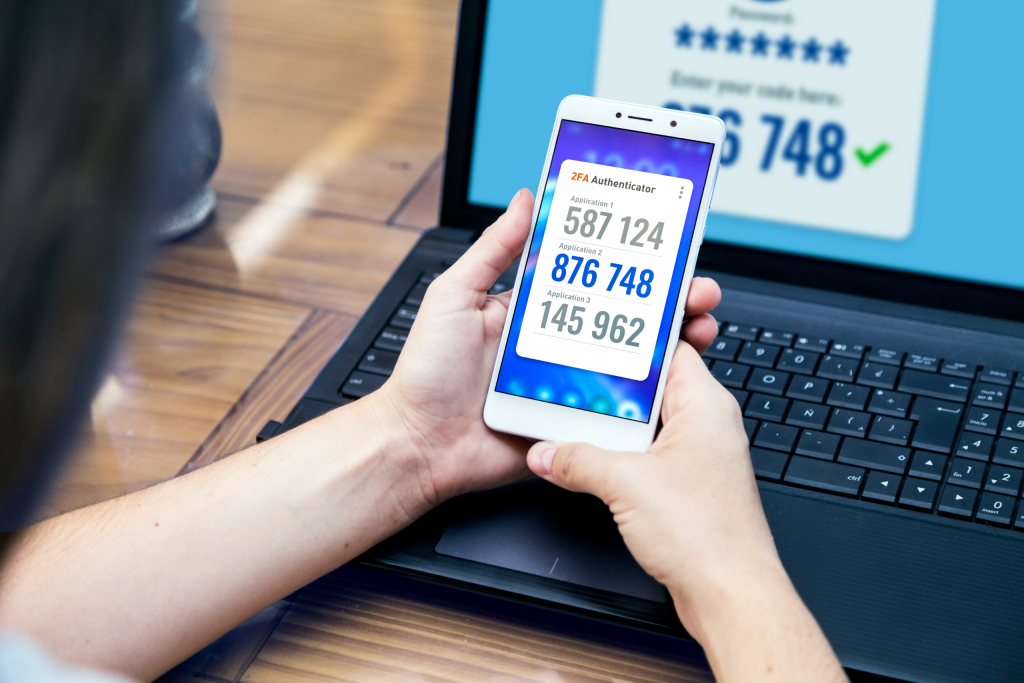
Older sign-in protocols such as POP and IMAP cannot prompt for MFA. Attackers know this and use them to skip the second factor entirely. Blocking legacy authentication closes that door.
Enforce that block through security defaults or a Conditional Access policy as core security controls, not as an optional setting. Before you switch it on, check your sign-in logs for old devices or apps that still rely on it. Scan-to-email on an older printer is a common example. Fix or replace those first so you do not break day-to-day work.
3. Use Conditional Access to Control How and Where People Sign In
Conditional Access lets you set conditional access policies about who can sign in, from where and on what device. It requires Entra ID P1, which is included in Business Premium. Sensible starting policies for a small business include:
- Require MFA for all users and all cloud apps
- Require MFA for every administrator role
- Block sign-ins from countries where you have no staff or customers
- Require a managed device that meets device compliance requirements to reach company data
These policies can also consider sign-in risk level as part of identity protection.
Start each policy in report-only mode. Unmanaged devices should usually be blocked or given limited access until they meet policy. It shows you who would be affected before you enforce anything, which avoids locking out a director on the way to the airport.
4. Lock Down Administrator Accounts
Administrator accounts are the most valuable targets in your tenant. Microsoft recommends fewer than five Global Administrators and says to manage access using least privilege through Role-Based Access Control, which you use to assign roles and limit access to only the permissions necessary for the task. In practice, that means three habits:
- Use the lowest role that does the job. Assign roles based on job need rather than broad standing admin rights, which also helps reduce insider threats. An Exchange Administrator does not need Global Administrator rights.
- Keep admin accounts separate. Administrators should use a dedicated admin account for admin work and a normal account for email and browsing.
- Set up two emergency access accounts. Microsoft recommends two cloud-only accounts with the Global Administrator role, kept for “break glass” situations. Store their credentials securely offline and alert on any sign-in.
5. Protect Email With Anti-Phishing and Email Authentication
Email is the front door for most attacks, and Microsoft blocks over 35 billion phishing threats annually. Defender for Office 365 Plan 1, included in Business Premium, adds Safe Links and Safe Attachments. These check links and files before your staff open them.
As part of that, advanced threat protection in Defender for Office 365 should be tuned as an ongoing email security control, not just switched on with default settings.
Turn on anti-phishing policies as well, with impersonation protection for your directors and finance team, since they are the people criminals pretend to be, to strengthen email security against evolving cyber threats.
Configure Exchange Online Protection to scan emails for malicious payloads and malware, and enable advanced threat protection before you set up your own domain records:
- SPF lists the servers allowed to send email from your domain.
- DKIM adds a digital signature that proves a message was not altered.
- DMARC tells receiving servers what to do with messages that fail those checks.
Start DMARC in monitoring mode, then move to enforcement once you are confident legitimate mail passes. This makes it much harder for criminals to send fake invoices that appear to come from your business.
6. Restrict Third-Party App Consent
When someone signs in to a third-party app with their Microsoft account, they can grant that app permission to read their mail or files. Attackers abuse this by sending a link to a malicious app that looks legitimate. Because the user approves it themselves, MFA never gets a chance to step in. We cover how this works in our guide to consent phishing in Microsoft 365.
In Microsoft Entra ID, you can stop users from consenting to apps from unverified publishers. You can also turn on an admin consent workflow, so requests go to an administrator instead of being approved by whoever clicks first. Review your list of enterprise applications at the same time and remove anything nobody recognises.
7. Manage and Secure Every Device With Intune and Defender for Business
A secure account on an insecure laptop is still a risk, because those devices access and expose email, collaboration tools, and file storage across Microsoft 365. Intune lets you set compliance rules for company devices, such as requiring encryption, a screen lock and an up-to-date operating system.
Stronger device management also improves your overall security posture. Defender for Business adds endpoint protection with detection and response, so suspicious activity on a device is spotted and contained.
The real value comes from linking the two to Conditional Access. A device that falls out of compliance can then be blocked from email and files until it is fixed. For personal phones, Intune app protection policies protect company data inside Outlook and Teams without taking control of the whole device.
8. Tighten SharePoint, OneDrive and Teams Sharing
Overshared files are a common weak point in small business tenants. Open sharing creates potential risks, including legal exposure when sensitive content is accessible more broadly than intended. A link that works for “anyone with the link” can be forwarded, guessed or picked up from an old email. Review these settings in the SharePoint admin center:
- Set the default sharing link to “specific people” rather than “anyone”.
- Limit external sharing to approved domains, or require guests to sign in.
- Set expiry dates on guest access and review guests every quarter.
- Remove departing staff and their shared links as part of offboarding.
This matters even more if you plan to use Microsoft 365 Copilot. Copilot can only surface what a person can already open, so loose permissions become loose answers. Our guide on whether Microsoft Copilot is safe for your business covers the preparation involved.
9. Label and Protect Sensitive Data
Sensitivity labels classify documents and apply protection, such as encryption or restricted sharing, based on how sensitive they are.
Data loss prevention (DLP) policies help protect sensitive data. However, implementing DLP policies requires strategic planning and oversight to ensure alerts and blocks align with real business use. This also supports compliance with regulatory requirements and industry standards where relevant.
Business Premium includes data protection features of this kind, though you should confirm exactly what your licence covers. Start small. Label your most sensitive folders first, then expand. Our guide to data loss prevention for SMBs in Australia explains how to set realistic policies without overwhelming your team.
10. Back Up Your Microsoft 365 Data Separately
Recycle bins and retention policies are designed for accidental deletion and data preservation for compliance needs. They are not a full backup.
They help meet governance requirements, but they are not a disaster recovery substitute. A compromised account, a malicious deletion or a ransomware attack can remove files, and that deletion can sync across every connected device.
Use a separate backup service that keeps copies of mailboxes, OneDrive, SharePoint and Teams data outside your tenant. Then test a restore at least once a year. A backup you have never restored is only a hope.
How to Track Your Microsoft 365 Security Best Practices With Secure Score
Once the ten steps are in place, you need a simple way to see what is still missing. Secure Score does that without any extra cost.
Where to Find Secure Score
Secure Score lives in the Microsoft Defender portal at security.microsoft.com. It comes with your Microsoft 365 subscription and does not need a separate licence to view. Organisations with more advanced monitoring needs can also feed Microsoft 365 signals into microsoft sentinel for broader threat detection and investigation.
It gives you a percentage score and a prioritised list of recommended actions. It only recommends actions for products you are licensed to use, so your list will look different on Business Standard than on Business Premium.
What a Good Score Looks Like
There is no universal target, and chasing 100% is rarely worth it. Some recommendations will not apply to your business, and others need extra licences. A better approach is to start with the high-impact items: MFA, blocking legacy authentication and tightening administrator roles.
Review the score monthly, or at least quarterly. Assign an owner to each open recommendation and note when it was completed. The Defender portal also lets you compare your score with similar organisations, which is a more useful benchmark than a global average. Regular review also supports audit readiness and helps maintain a stronger security posture over time.
How These Steps Support the Essential Eight and SMB1001
Good Microsoft 365 settings also move you toward the frameworks Australian customers and insurers increasingly ask about.
Mapping to the Essential Eight
The Australian Signals Directorate’s Essential Eight lists eight mitigation strategies. These include patching applications, patching operating systems, multi-factor authentication, restricting administrative privileges, application control, restricting Microsoft Office macros, user application hardening, and regular backups.
Several of the steps above line up directly. MFA covers steps 1 to 3. Restricting administrative privileges is step 4. Device policies in step 7 help enforce patching and Office settings. Regular backups are step 10.
Microsoft 365 settings alone will not earn you a maturity level, because the Essential Eight assesses your whole environment. They do give you a strong foundation. Our guide to the Essential Eight for SMBs explains what each maturity level expects.
A Practical Foundation for SMB1001
SMB1001 is an Australian cybersecurity standard built for small and medium businesses. Compliance work also depends on audit logging so audit logs track user and administrator activity for investigation, evidence, and compliance.
Keeping audit trails in place also supports incident response and helps meet governance expectations. XCD IT holds SMB1001 Gold certification. A well-configured Microsoft 365 tenant is a practical place to start if your customers, insurers or suppliers are asking you to show how you manage cybersecurity risk.
How XCD IT Helps Brisbane SMBs Apply Microsoft 365 Security Best Practices
Knowing the steps is one thing. Applying them without disrupting your team is another. This is where a local Microsoft Partner earns its keep.
Setup and Hardening From a Microsoft Partner
XCD IT is a Microsoft Partner serving Brisbane, the Gold Coast and the Sunshine Coast. We can review your Microsoft 365 tenant against the steps in this guide, switch on the controls in a safe order and document what changed. That way, a new Conditional Access policy does not lock your team out on a Monday morning. Explore our Microsoft 365 services to see what is involved.
Ongoing Monitoring and Review
Microsoft 365 security is not a one-off project, and ongoing review should cover logs, alerts, permissions, and changes in your Microsoft 365 environment. Staff join and leave, new apps appear and settings drift.
Want these steps handled for you? See our cybersecurity services for Brisbane businesses.
In many cases, large enterprises have dedicated teams for this, while SMBs usually need outside support to maintain the same consistency. XCD IT’s bundled managed IT and cybersecurity plans, commonly priced between AU$100 and $250 per user per month, are built to cover this ongoing work rather than leaving it to whoever has spare time.
Ongoing monitoring in tools like Microsoft Defender XDR can surface threats earlier and speed response. Not sure where your tenant stands today? Start with our cyber assessment form, or contact the team to talk through your Microsoft 365 setup.
Frequently Asked Questions Microsoft 365 Security Best Practices

- 8+ Best Cybersecurity Companies in Brisbane (2026 Guide for SMBs) - November 7, 2026
- 20 Best Managed IT Service Companies in Brisbane (2026 Guide for SMBs) - November 7, 2026
- Co-Managed IT: How It Works With Your In-House IT Team - November 4, 2026


